

The phone rings at the front desk. The caller says he’s from Microsoft, or your bank, or “the IT company,” and he’s seen a problem with your computer. He just needs you to open a website and type in a short code so he can take a look. Searches for fake remote support Fort Myers help usually start right after that call, once someone notices the mouse moving on its own.
This scam isn’t new, but it has gotten smoother. The tools the scammers use are the same legitimate remote access programs real IT teams use every day. That’s exactly why they work. Nothing about the software looks suspicious, so antivirus often lets it right through.
How the scam usually starts
We see it come in three main ways. The first is the cold call. Someone claims to be from a big tech company, your internet provider or your IT support and says your computer is infected, your license expired or your account was hacked.
The second is the pop up. A browser window suddenly fills the screen with a warning, a loud alarm and a phone number to call. We wrote about one version of this in our post on the fake McAfee pop up. When you call the number, the person on the other end walks you through installing a remote access tool.
The third is the email. It looks like a renewal notice or an invoice for something you never bought, with a “support” number to call to cancel. Same ending. They need to connect to your computer to “process the refund.”
Why remote access tools are the real prize
Once a stranger has remote access, they can see everything on the screen and control the mouse and keyboard. They can open your email, your bank’s website, your patient or client records and your files. Some of them stage a fake refund, claim they sent too much money, and pressure your employee to send the “difference” back by wire or gift cards.
The worse version is quieter. The scammer installs a second remote tool in the background and leaves it there, so they can come back later, after hours, when nobody is watching. The federal Cybersecurity and Infrastructure Security Agency has warned about exactly this, attackers using normal remote management software to get in and stay in. Their advisory on malicious use of remote monitoring software is worth a read if you want the technical details.
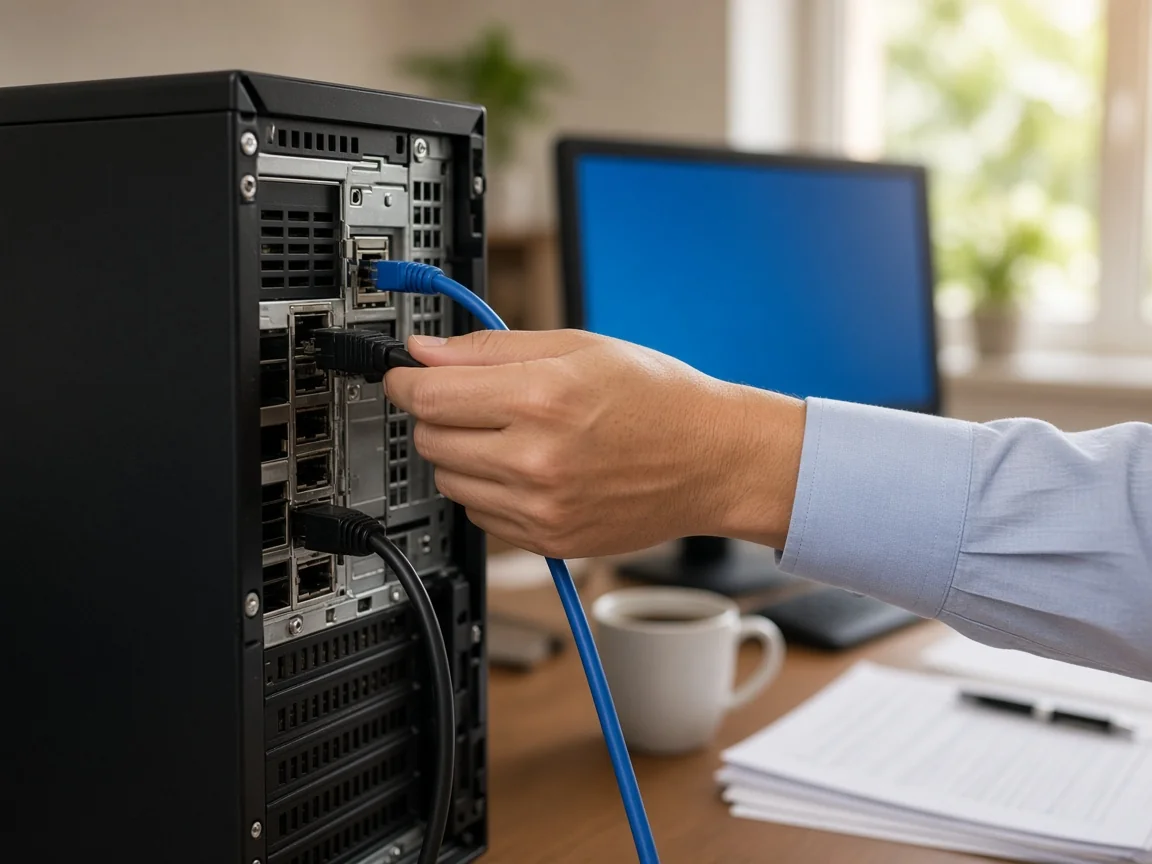
Fake remote support Fort Myers offices should watch for
Here are the red flags we tell every client and their staff to look for.
- They called you. Microsoft, Apple and your bank do not call out of the blue to fix your computer.
- There’s a rush. “Your data will be deleted in 30 minutes” is pressure, not support.
- They want a code or a download. Any request to visit a website and enter a code, or install a program so they can “connect,” should stop you cold.
- They want payment in odd ways. Gift cards, wire transfers, crypto or a “refund” that needs money sent back are always a scam.
- They know a little about you. Scammers often have your name, your business name or the name of your IT provider from public sources. Knowing a detail doesn’t make them real.
The simplest rule is this. If someone reaches out to you and asks for access to a computer, hang up and call your IT provider at the number you already have. Not the number they gave you.
How to know it’s really your IT team
Real support should be boring and predictable. Your staff should know who your IT provider is, how to reach them and what tool they use to connect. When our team connects to a client computer, it’s because the client asked for help, and we use one tool that’s already set up on our remote support page.
A few habits make this much easier to spot:
- Post your IT provider’s phone number at every front desk and in your onboarding notes.
- Agree on one remote tool and remove any others that aren’t approved.
- Have staff ask a callback question, like “What’s our ticket number?” or “Who do you normally talk to here?”
- Don’t give employees admin rights they don’t need. Most remote tools need admin rights to install.
What to do if someone already got in
If a stranger connected to one of your computers, act fast but stay calm.
- Disconnect from the internet. Unplug the network cable or turn off WiFi on that computer. Don’t shut it down yet if you can avoid it, because that can make it harder to see what happened.
- Call your IT provider. They need to find and remove anything the scammer installed, including hidden remote tools.
- Call your bank. If they saw or touched banking or payment pages, ask the bank to watch for or stop transfers.
- Change passwords from a different device. Start with email, banking and anything the person typed while they were connected. Turn on multifactor sign in if it isn’t on already.
- Write down what happened. The phone number, the time, what they said and what was on the screen. This helps your IT team, your bank and your cyber insurance carrier.
Don’t feel embarrassed if it happens to your office. These callers are professionals, and they target busy front desks on purpose. The offices that come out fine are the ones that report it right away.
Train your staff before the call comes
Most of these scams are beaten by one person at the front desk saying “Let me call you back.” That only happens when people know what to expect. A short refresher at a staff meeting goes a long way, and our security awareness training covers phone scams like this along with phishing email.
On the technical side, a good IT provider can also block unapproved remote access tools from installing at all, alert on new software and lock down admin rights. That way even if someone gets talked into clicking, the scammer hits a wall.
Want a second set of eyes?
HenkTek helps offices across Southwest Florida, including Cape Coral, Bonita Springs and Naples, keep strangers off their computers. If you’re not sure what remote tools are on your machines, or you think someone may have gotten in, reach out to our team or call us at (239) 234-2334.




HenkTek is a local IT company in Fort Myers that looks after the technology Southwest Florida businesses depend on, from Cape Coral and Bonita Springs to Naples. We handle managed IT, cybersecurity, backups and help desk support, and we explain things in plain English.